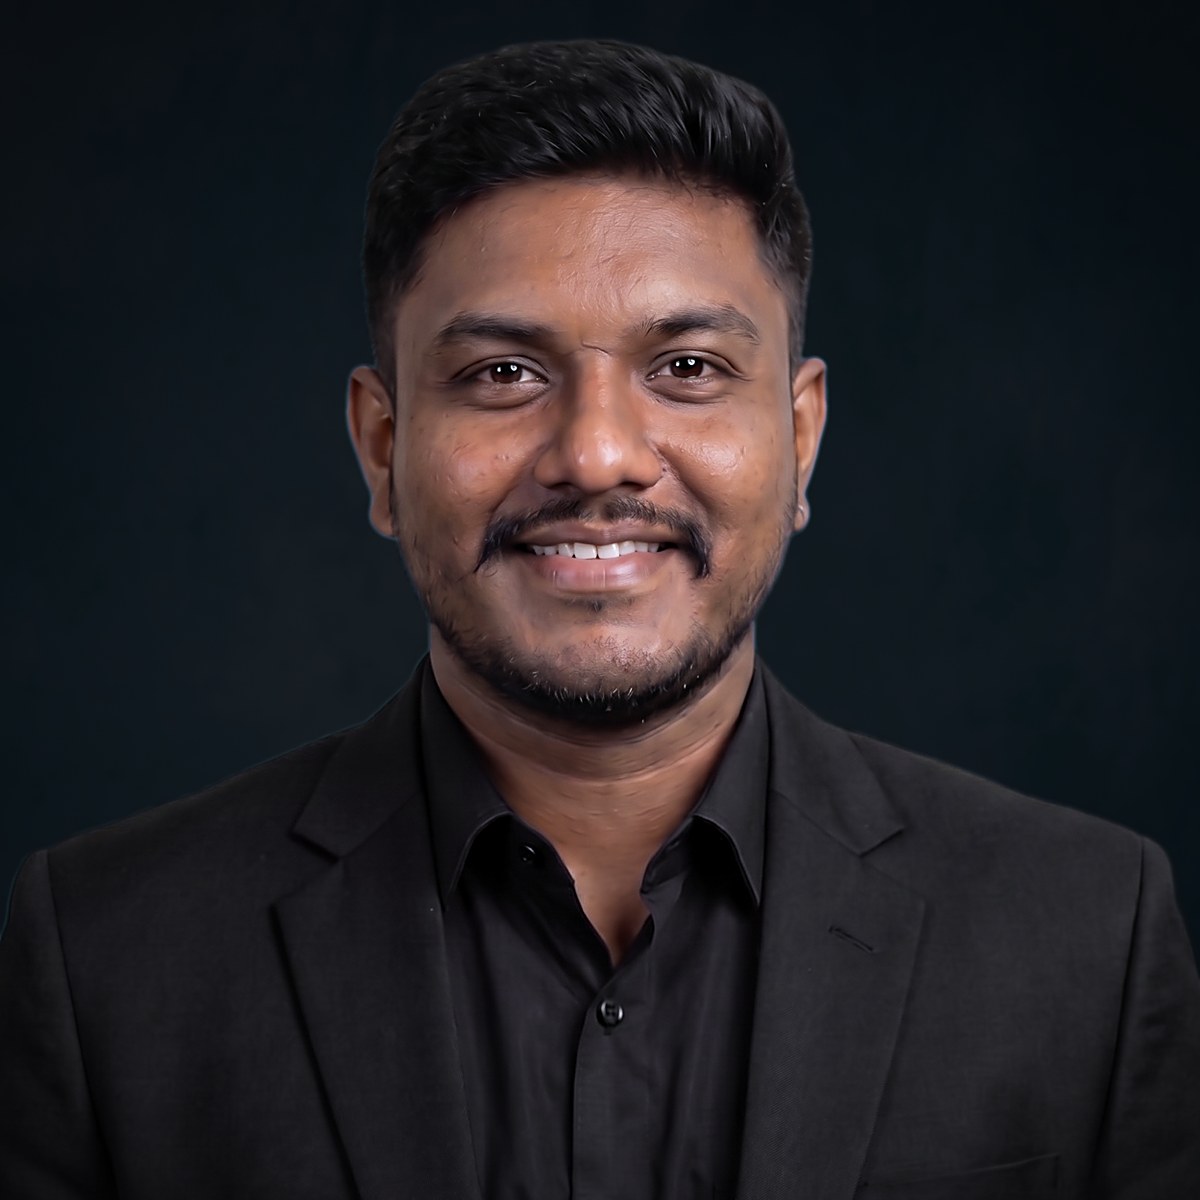
Every finding starts as a question.

ADITYA K CHHAYA

~$_

“Breaking things to make them secure.” I think like an attacker so your systems don't have to find out the hard way.

THREAT LEVEL ▸ LOW//OWASP TOP 10 ✓ COVERED//CVE-2024-3094 ▸ MITIGATED//PORTS 1–1024 ▸ SCANNED//PAYLOAD ▸ AES-256-GCM//RECON ▸ ACTIVE//0xDEADBEEF · 0xC0FFEE//BURP SUITE ▸ INTERCEPTING//PRIV-ESC ▸ ENUMERATING//FLAG ▸ CAPTURED//
//case file // background

Aditya K Chhaya

$ I work with a break-to-fix mindset, approaching security the way an attacker would so systems get hardened before anyone else finds the gaps. My focus is offensive security: web and application penetration testing, network exploitation, and vulnerability research, with 100+ engagements behind me across professional roles, internships and independent projects. The part that matters is what comes after, turning findings into remediation a team can actually act on. I keep sharpening through CTFs, labs, and hands-on work.

I gravitate toward offensive security. There is a real thrill in probing an application, chaining small misconfigurations into something with actual impact, then writing it up so a team can close it for good. Every engagement, CTF, and lab is another rep at sharpening that instinct.

Mindset
Break-to-fix
100+
VAPT Projects
Top 10
OWASP
Certified
CEH
Location

GIFT City, Gandhinagar · Rajkot, Gujarat, India

Languages

English · Hindi · Gujarati

Education
  • B.Tech in Computer Science / Cyber SecurityParul University
  • Diploma in Computer EngineeringGTU (Gujarat Technological University)
//career // record

Operational History

Sep 2026 to presentIn progress

MSc in Cyber Security

De Montfort University, Cyber Technology Institute · Leicester, UK

Currently reading for the MSc. Deepening the offensive skill set with advanced security research, digital forensics and enterprise-scale defence, from the UK.

//inventory // field kit

Tooling and tradecraft logged from live engagements. Pick a category to filter the records.

Web & App Pentesting

  • OWASP Top 1092%
  • Burp Suite90%
  • SQLi / XSS / SSRF88%
  • Authentication & Session Flaws85%
  • API Security Testing80%

Network & Infrastructure

  • Nmap90%
  • Metasploit84%
  • Nessus82%
  • Privilege Escalation80%
  • Active Directory Attacks75%

AI & Agent Automation

  • Multi-Agent Orchestration88%
  • MCP Tooling & Integrations85%
  • Automated Recon Pipelines86%
  • Agent Tool & Prompt Design82%
  • Quality Gates & Output Validation78%

Mobile & Wireless

  • Android App Testing78%
  • Traffic Interception (Burp/ADB)80%
  • Wireless Recon72%

Tools & Platforms

  • Kali Linux90%
  • Wireshark82%
  • Python Scripting84%
  • Git / Linux CLI86%

Soft Skills

  • Technical Reporting88%
  • Communication85%
  • Problem Solving92%
  • Continuous Learning95%
//rules of engagement

Operations

ENGAGEMENT LIFECYCLE
01

Reconnaissance

Map the attack surface first. OSINT, subdomain enumeration, fingerprinting, and asset discovery, all before a single payload is fired.

OSINTSubdomain EnumFingerprinting
MODULE READY
02

Web App Pentesting

Hunt OWASP Top 10 and past it. SQLi, XSS, SSRF, auth flaws, business logic, then chain them into real, demonstrable impact.

OWASPBurp SuiteLogic Flaws
MODULE READY
03

Network Exploitation

Scan, enumerate, and pivot. Service exploitation, misconfig abuse, and lateral movement across internal infrastructure.

NmapMetasploitPivoting
MODULE READY
04

Privilege Escalation

From foothold to root. Local enumeration, kernel and misconfiguration abuse, and credential harvesting to own the host.

Linux/WindowsKernelCreds
MODULE READY
05

Reporting & Remediation

Translate findings into clear, prioritized, business-aware reports with reproducible PoCs and fixes a team can act on.

CVSSPoCRetest
MODULE READY
scroll
//evidence locker

Selected operations, documented like evidence: the challenge, the approach, the outcome.

project / 0101

AI-Powered Penetration Testing Orchestrator

Multi-agent automation system for end-to-end VAPT execution

An intelligent orchestrator-driven system that automates full penetration tests from reconnaissance through reporting. Coordinates parallel specialist AI agents through a gated wave pipeline with real-time evidence tracking, quality gates, and CVSS-scored findings generation.

Challenge

Building reliable autonomous agents that self-verify coverage, maintain accuracy across parallel execution, and catch under-tested attack surfaces before report generation.

Outcome

A working pipeline that runs recon-to-report unattended, self-checks its own coverage through quality gates, and outputs CVSS-scored, evidence-backed findings. The same orchestration approach placed 9th with a full 37/37 clear at Hack The Box's MCP TryOut.

AI OrchestrationMulti-Agent SystemsPythonJSON Schema Validation
project / 0202

Perimeter: Automated Recon Framework

One-command external recon, from subdomains to secrets

A bash pipeline that takes one target and runs full external recon: subdomain enumeration, live-host probing, port scanning, endpoint discovery, and JS/secret hunting. It has passive, standard, and full scan modes.

Challenge

Chaining a dozen+ third-party recon tools into one reliable pipeline that degrades gracefully when a tool is missing, and keeping results scoped to the real target.

Outcome

One command turns a bare domain into a structured findings directory containing subdomains, live hosts, open ports, endpoints, and flagged secrets, ready for manual triage.

BashPythonNucleihttpx / subfinder
project / 0303

Online Face Recognition & Attendance System

Edge-deployed biometric attendance on Raspberry Pi

A real-time face-recognition attendance platform running on Raspberry Pi. Captures faces via camera, matches against an enrolled dataset, and logs attendance to a web dashboard built with Flask.

Challenge

Achieving reliable recognition on constrained edge hardware, handling varying lighting conditions, and keeping latency low enough for live capture.

Outcome

Delivered an end-to-end working system with a web interface for enrollment, live recognition, and exportable attendance records.

Raspberry PiPythonOpenCVFlaskSQLite
project / 0404

CryptoWorld: Cryptography Learning Platform

Interactive playground for classical & modern crypto

A Flask web app that teaches cryptography hands-on, with interactive cipher tools, encrypt/decrypt demos, and plain explanations of the core concepts for learners and security students.

Challenge

Designing intuitive interactive tooling for complex cryptographic concepts while keeping the implementation correct and educational.

Outcome

Built a usable learning platform that demystifies ciphers and crypto fundamentals through interactive, in-browser demonstrations.

PythonFlaskJinja2JavaScript

_ further case files pending declassification

//credentials on record

Verified and current. Earned the practical way, not the multiple-choice way.

Key
CEH

CEH v12 (Practical)

EC-Council

credential held
Key
CNSP

Certified Network Security Practitioner

The SecOps Group

credential held
GCC

Google Cybersecurity Certificate

Google / Coursera

credential held
CTF

Capture The Flag Competitor

Multiple Platforms

credential held
//after-action report

Leaderboards, disclosures, and independent engagements worth putting on the record.

100+ Web Application VAPT Engagements

100+ web and application penetration tests to date, spanning professional roles, internships and independent projects. OWASP Top 10 issues and business logic flaws, each mapped to a prioritized remediation path.

Rank 9 at Hack The Box MCP TryOut

Built an agent orchestrator that captured every flag in HTB's AI-agent CTF. A full 37/37 clear, placing 9th on the global scoreboard (Apr 2026).

3rd Place at CEH Global CTF

Placed 3rd in EC-Council's global Capture The Flag competition against international competitors.

Bug Bounty & Responsible Disclosure

Active in vulnerability research and responsible disclosure across public programs (HackerOne).

Freelance Security Assessments

Independent penetration testing and security consulting for small businesses and indie products.

Web Pentesting★Network Exploitation★OSINT★Privilege Escalation★Responsible Disclosure★CTF★Threat Modeling★Web Pentesting★Network Exploitation★OSINT★Privilege Escalation★Responsible Disclosure★CTF★Threat Modeling★
//final transmission

Direct line, no gatekeepers. Messages land straight in my inbox.

aditya@portfolio : ~/contact
aditya@portfolio:~$ ./connect.sh
establishing secure channel ... ok
Answer 3 prompts and I'll route your message.
tip: press Enter to submit · type 'clear' to restart
1/3 who's reaching out? (your name)
name ›
building connectionslive
[NEW]connection · security researcherBerlin
[+]friend request accepted
[OK]collab synced · bug bounty crew
[NEW]intro made · recruiterAmsterdam
[★]opportunity · red team role